Security
- SecurityProject
cvs-fast-export 2.1 fixes invalid-delta errors for binary blobs
cvs-fast-export converts RCS or CVS history into a fast-import stream. Version 2.1 repairs an “invalid delta” error when processing binary blobs.
Engineers migrating or inspecting legacy CVS histories can use the release to handle affected binary blobs.
- SecurityProject
CAI: An Open-Source Framework for AI Security Operations
CAI is an open-source framework for AI-powered cybersecurity operations, including multi-agent workflows, security tools, CTF automation, vulnerability discovery, and AI red teaming. It supports MCP integrations with Burp Suite and external tooling.
Engineers can explore a framework for applying AI agents to security testing and research workflows.
Bootloader Security: Attack Surfaces, Detection, and Defenses
A paper covers bootloader attack surfaces, vulnerability detection techniques, and defenses across firmware, OS, and monolithic bootloaders.
Engineers can use its overview to assess bootloader risks and defensive approaches across different boot architectures.
- SecurityArticle
GPS Special-Message Field May Reveal Cryptographic Logistics Metadata
A post says a publicly broadcast 176-bit GPS navigation field has carried high-entropy payloads for years. It suggests the field may function as a one-way encrypted control or key-distribution channel, but does not establish that interpretation.
Engineers assessing GPS signal security may want to investigate what operational metadata these broadcasts expose.
- SecurityPaper
A self-replicating AI worm adapts across vulnerability classes
The post describes a research worm that uses an open-weight LLM on compromised GPU machines and adapts its attack logic. In corporate testbed trials, it reportedly exploited systems and replicated across Linux, Windows, and IoT targets.
Engineers should assess how adaptive agents could change vulnerability response and network containment.
- SecurityPost5 months ago @lukOlejnik
Post warns of AI-orchestrated intrusion workflows
The post argues that agentic orchestration of models with scanners, shells, and other tools could make intrusion workflows more repeatable and cheaper. It urges defenders to expect continuous AI-assisted attempts.
It highlights orchestration, tool access, and adaptive retries as security concerns for defenders.
- SecurityArticle
Collision Attacks on SHA-2 Extended to 39 Steps
The paper presents an improved search procedure for SHA-2 collision attacks. Its preview says prior work reached 37 steps but could not reach 38 because of a low-probability uncontrolled part in the differential characteristics.
Engineers assessing SHA-2’s security can track progress in cryptanalysis, while keeping these reduced-step results distinct from attacks on full SHA-2.
- SecurityProject
Cybersecurity resources: posts, papers, and tools
A GitHub awesome list collecting cybersecurity blog posts, writeups, papers, and tools.
It offers engineers a starting point for discovering cybersecurity resources.
- SecurityProject
MogVMP statically devirtualizes VMProtect 3.0–3.5
MogVMP is a static devirtualizer that lifts VMProtect-virtualized code to LLVM using Remill, then removes the VM layer through optimization. The author says the approach lifts the VM’s full x86 code.
It offers engineers a codebase for studying static devirtualization and LLVM-based reverse engineering.
- SecurityPaper
Browser SSD Timing Side Channel Enables Activity Fingerprinting
The linked paper describes using the browser’s Origin Private File System to measure SSD latency from a regular tab. The post reports 88% accuracy for identifying visited sites and 95% for detecting launched desktop apps.
Engineers can assess how storage contention may expose cross-application activity without permissions or native code.
- SecurityArticle
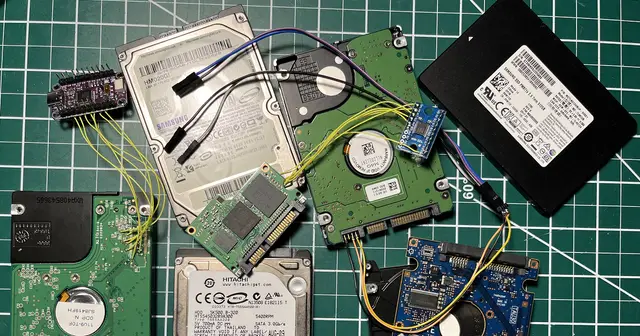
HDD Firmware Hacking: Dumping, Analysis, and Modification
A series on dumping, reverse engineering, and modifying firmware on HDDs and SSDs. The post also mentions debugging via JTAG.
It offers engineers a look at firmware-level analysis and modification of storage devices.
- SecurityArticle
Post alleges legal-data extraction and WhatsApp automation tool
The post alleges that ADV INFINITY extracts court cases, enriches data with Serasa information, and sends WhatsApp messages. It describes HWID licensing and a central heartbeat every 30 seconds.
The described features raise security and privacy concerns around large-scale collection and handling of personal data.
- SecurityProject
C2IntelFeeds provides feeds of suspected and verified C2 infrastructure
C2IntelFeeds is a repository of automatically generated C2 infrastructure feeds based on large-scale internet scanning data. It includes IPs, domains, URL paths, port combinations, and configuration metadata where available.
Engineers can use the feeds for threat hunting and SIEM enrichment, while validating unverified indicators before blocking.
- SecurityProject
OpenVul: A Framework for LLM-Based Vulnerability Detection
OpenVul is an open-source post-training framework for LLM-based vulnerability detection. Its GitHub repository describes the project.
Engineers can review the framework as a resource for LLM-based vulnerability detection.
- SecurityProject
Linux kernel security and exploitation collection updated
The Linux kernel exploitation collection has January and February updates, adding links related to Linux kernel security and exploitation.
Engineers can use the collection to find resources on Linux kernel security and exploitation.
- SecurityVideo
Limitations of Ultrasonic Microphone Jammers
The post questions claims made for a portable audio jammer, comparing it with existing ultrasonic jammers and DIY kits. It notes possible limits involving device detection, range, room reflections, fabric, and obstructions.
Engineers evaluating privacy hardware should account for detection and acoustic constraints before relying on a jammer.
- SecurityArticle
Praetorian’s Multi-Agent Pipeline for CVE Detection Templates
Praetorian describes a multi-agent pipeline that turns CVE research into validated Nuclei detection templates. It uses specialized agents, three model providers, and an actor-critic refinement loop.
Engineers can learn how AI agents are orchestrated to research vulnerabilities and produce validated detection templates.
- SecurityProject
Darkweb Scanner for Keyword Monitoring on .onion Sites
The post describes osintph/darkweb-scanner as a keyword monitoring tool for .onion sites, intended for threat intelligence and brand monitoring. The linked GitHub page previews a threat intelligence and OSINT platform.
Engineers evaluating threat intelligence tooling can inspect the linked project and its stated scope.
- SecurityArticle
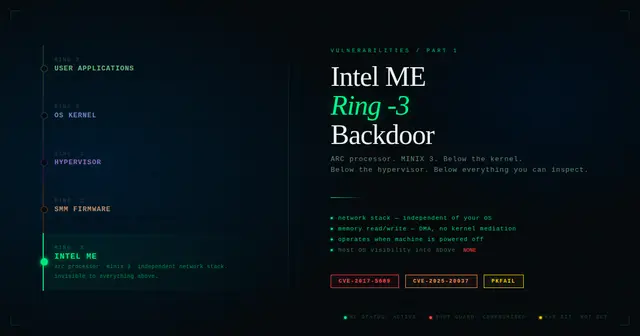
Technical analysis of Intel Management Engine vulnerabilities
The article examines Intel Management Engine architecture and firmware, CVE-2017-5689 exploitation, a CVE-2025-20037 TOCTOU race condition, PKfail, and detection methods.
It offers engineers technical context on Intel ME attack paths and detection.
- SecurityArticle
Secure deletion in magnetic and solid-state storage
Peter Gutmann’s 1996 paper discusses data remanence and secure deletion from magnetic and solid-state memory, including the limits of simply overwriting data once on magnetic media.
It highlights why storage media and deletion methods matter when designing data sanitization procedures.