Security
- SecurityDocs
Google FLARE Malware Analysis Crash Course Document
A Google Docs guide titled Malware Analysis Crash Course, by Jae Young Kim and Nick Harbour of the FLARE Learning Hub. Its preview lists chapters from x86 basics through instruction basics.
A structured free resource for learning malware analysis, from x86 assembly fundamentals upward.
- SecurityProject
Hardening a rooted LG webOS TV against microphones and telemetry
A GitHub project that hardens a rooted LG webOS TV: it disables microphones and the remote-mic voice pipeline, blocks ad, telemetry and ACR endpoints, and hides ad apps.
Useful for engineers who want a concrete example of privacy hardening on an embedded smart TV OS.
- SecurityPost21 days ago @ProgrammerDude
Author says short-lived bearer tokens need proof of possession
The author argues that OIDC bearer tokens with 15-minute expiration will not stop attackers from getting owned, and that proof of possession such as TLS binding is the only real fix. They also predict OIDC will be dead soon.
Shows why short token lifetimes alone do not stop token theft; consider sender-constrained tokens.
- SecurityPost21 days ago @always_ff_rohan
Private CA roots like Zscaler can mint unlogged certs for any domain
The author argues that TLS inspection roots installed on corporate laptops can issue certificates for any site without certificate transparency logging, because browsers only enforce timestamps for publicly trusted CAs. No links or sources are provided.
Explains a real trust gap: locally installed roots can impersonate domains invisibly, which matters for endpoint and TLS inspection threat models.
- SecurityArticle
Post claims iOS IPA decryption without a physical iPhone
The post links to a report about decrypting FairPlay-protected iOS IPAs, claiming the process works without a physical iPhone or jailbreak.
The claim may interest engineers studying iOS app protection and reverse engineering.
- SecurityPaper
How to Back Up High-Value Secret Keys
The post links to a paper about backing up high-value secret keys.
Secret-key backup is a security engineering concern for systems that depend on valuable keys.
- SecurityProject
Practical cryptography course covers PIR and TLS
A practical cryptography course covering PIR in practice, TLS 1.3, post-quantum integration, and TLS attestation.
Engineers can use it to explore practical cryptography topics and TLS features.
- SecurityArticle
Signing TLS Handshakes Inside a TPM in Go
The article shows how to use a client certificate whose private key stays in a TPM, covering what Go's crypto/tls requires and the cost per handshake.
Useful for engineers evaluating TPM-backed client keys and their performance impact in Go TLS connections.
- SecurityArticle
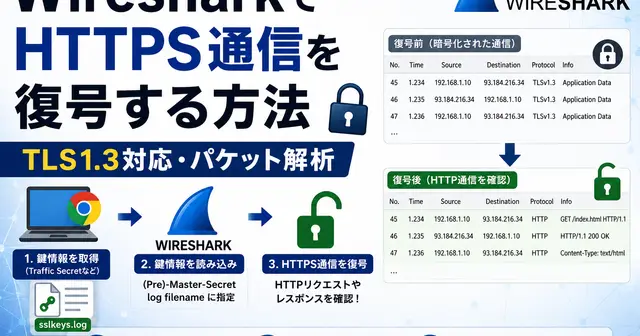
Decrypt TLS 1.3 HTTPS traffic in Wireshark
The blog explains how to use SSLKEYLOGFILE to capture TLS key information and load it into Wireshark to inspect HTTP requests in captured HTTPS traffic.
Useful for engineers troubleshooting and analyzing HTTPS traffic they are authorized to inspect.
- SecurityPaper
Study reports code overlap between Geedge leak and Great Firewall
The post links to a USENIX Security paper whose authors report source-code overlap between leaked Geedge Networks code and China's Great Firewall, including DNS and RST injection behavior.
The reported overlap may help engineers understand how network filtering systems implement traffic injection.
- SecurityPaper
IO Factory simulates AI-enabled influence campaigns
The paper introduces IO Factory, an AI-driven framework for simulating information and influence campaigns as integrated, traceable processes. It describes coordinated AI agents that adapt to platform feedback and disguise campaigns as ordinary social interaction.
Security teams can use the work to study coordinated, adaptive influence campaigns that are difficult to detect from individual messages.
- SecurityPaper
ExploitGym evaluates AI agents’ ability to exploit vulnerabilities
ExploitGym studies whether AI agents can turn security vulnerabilities into concrete impacts such as unauthorized file access or code execution. The task requires low-level program reasoning, runtime adaptation, and sustained progress.
It offers a way to evaluate AI agents’ capabilities for converting vulnerabilities into real attacks.
- SecurityPost3 months ago @T3chFalcon
How reverse-proxy phishing can capture MFA session cookies
The post describes phishing kits that proxy a victim’s login and MFA interaction with a real service, then intercept the resulting session cookie. It names Evilginx, Modlishka, and Muraena.
Engineers can use this attack pattern to inform phishing defenses and authentication design.
- SecurityProject
obfus.h: Compile-time obfuscation for C
obfus.h is a macro header for compile-time C obfuscation on Windows x86/x64 using tcc. The post says it supports virtualization, anti-debugging, and control-flow obfuscation.
Engineers can assess its code-mutation techniques when evaluating software protection and reverse-engineering resistance.
- SecurityPaper
Practical Privacy and Availability Attacks on 4G/LTE
A 2015 paper by Altaf Shaik et al. examines practical attacks against privacy and availability in 4G/LTE mobile communication systems.
Relevant to engineers assessing privacy and availability risks in mobile networks.
- SecurityPost3 months ago @UK_Daniel_Card
Device-code phishing is not specific to Wi-Fi
The author argues that device-code authentication phishing can happen over Ethernet or the internet, not only over Wi-Fi.
It cautions engineers against treating device-code phishing as a Wi-Fi-specific risk.
- SecurityArticle
DeepSec Benchmark Compares Models for Vulnerability Discovery
The post reports private benchmark results for Kimi K3 and other models using DeepSec, an open-source harness for finding vulnerabilities in large codebases. It compares recall, precision, and cost on an undisclosed open-core application.
The results offer a cost-and-performance comparison for engineers evaluating models for security analysis.
- SecurityPost3 months ago @charliermarsh
uv can check packages against OSV before installation
Setting `UV_MALWARE_CHECK=1` makes uv cross-reference the OSV database before installing packages from a remote registry and block packages reported as malware.
This adds a malware check before package installation from remote registries.
- SecurityPost4 months ago @0x0SojalSec
Prompt injection in AI-assisted binary reverse engineering
The post describes Naval Postgraduate School research on embedding short prompt-injection strings in C binaries to influence LLM-powered reverse-engineering agents during Ghidra analysis. It says the researchers used an AutoDAN-style genetic algorithm to generate payloads that fit Ghidra’s…
Engineers using AI for binary analysis should consider that strings in analyzed binaries can act as untrusted instructions to the model.
- SecurityProject
Anthropic’s Reference Harness for Security Scanning and Patching
The repository provides skills for threat modeling, scanning, triage, and patching, plus a customizable autonomous scanning harness.
Engineers can explore a reference workflow for security analysis and vulnerability remediation.
 arxiv.org