io.github.jyswee/authshore
Auth infrastructure for coding agents. User pools, secrets vault, token management. As easy as git.
Open source Repository Open in the app JSON README (API)
About
Auth infrastructure for coding agents. User pools, secrets vault, token management. As easy as git.
Details
- Kind
- MCP servers
- Topic
- Cloud & DevOps
- Publisher
- jyswee
- Origin
- official
- Category
- ferramentas
- Transport
- sse
- Version
- 1.0.3
- Last push
- 2026-07-31T22:52:06Z
- Repository state
- ativo
- License
- NOASSERTION
- Added
- 2026-08-29 04:00:18
- Updated
- 2026-08-29 04:00:18
- Origin id
io.github.jyswee/authshore
README
# as
[](https://www.npmjs.com/package/authshore)
[](https://registry.modelcontextprotocol.io)
[](#remote-mcp--zero-install)
**Auth infrastructure for coding agents — user pools, secrets vault, token management. As easy as git.**
> **git for your code. as for your auth.**
Your agent can scaffold a whole app in an afternoon — then stalls the moment it needs auth. It hardcodes secrets into `.env` files it later commits, rolls its own JWT handling, and leaves you wiring up Cognito by hand. AuthShore is the auth layer your agent runs itself: one install, and it provisions user pools, stores secrets encrypted, and mints, validates and refreshes tokens — from the terminal, with no console to click through.
**Works with:** Claude Code · Cursor · Cline · Windsurf · Aider · Codex · any MCP client
## See It In Action
Real terminal sessions against the live API — click a GIF for the full video.
| Zero to auth in 60s | Secrets vault | Tokens & pools |
|---|---|---|
| [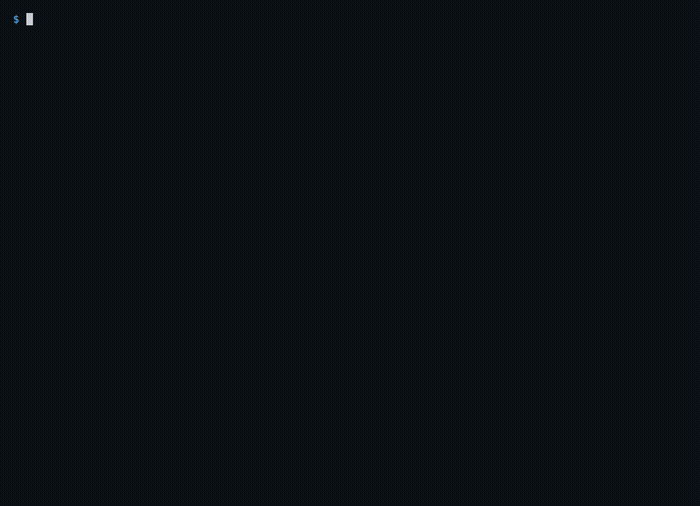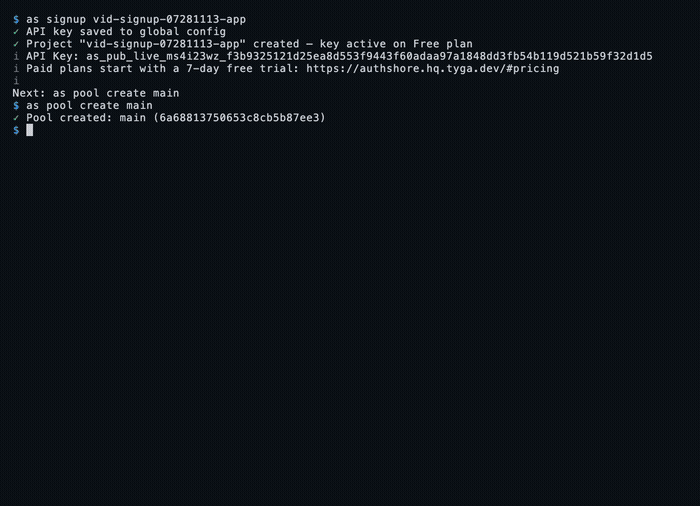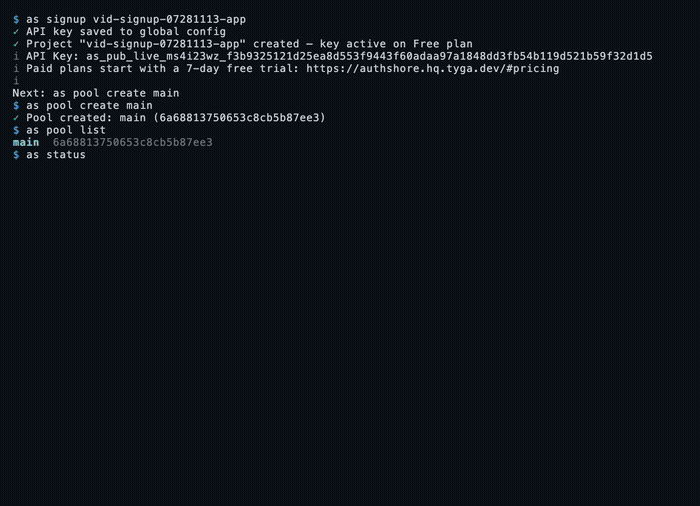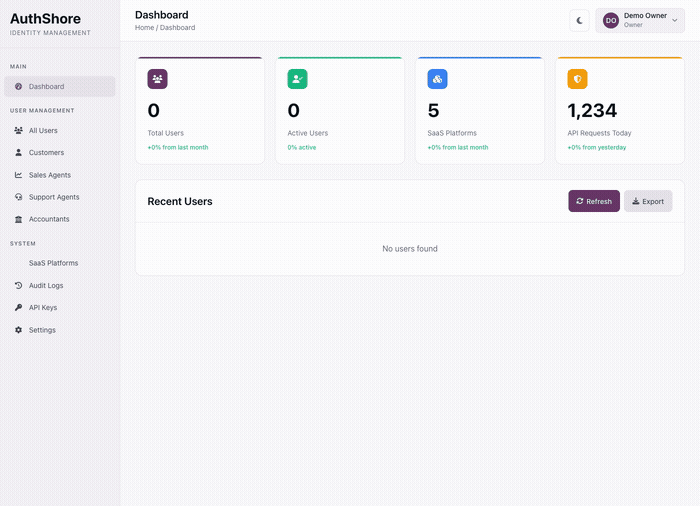](https://prodmedia.tyga.host/public/tyga.cloud/landing/authshore.ai/demo/signup-demo.mp4) | [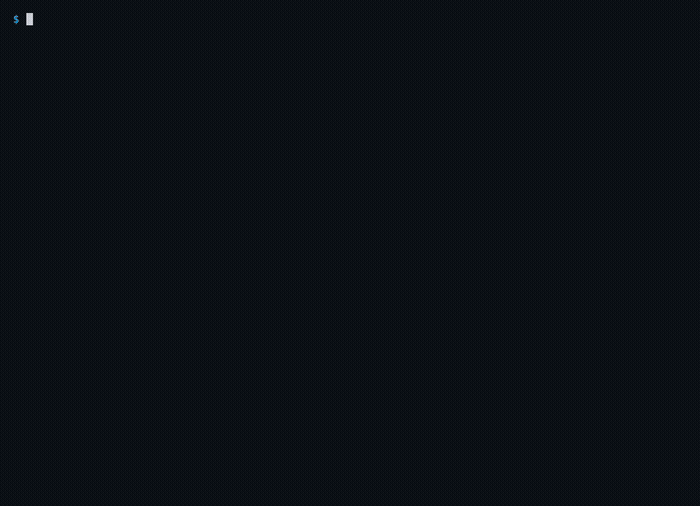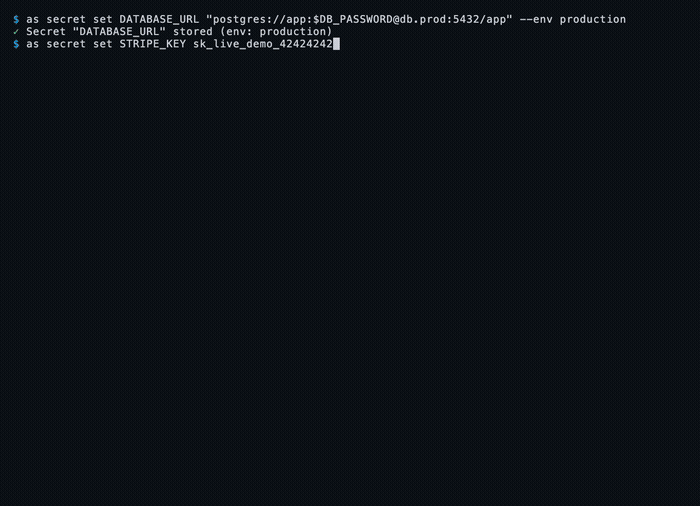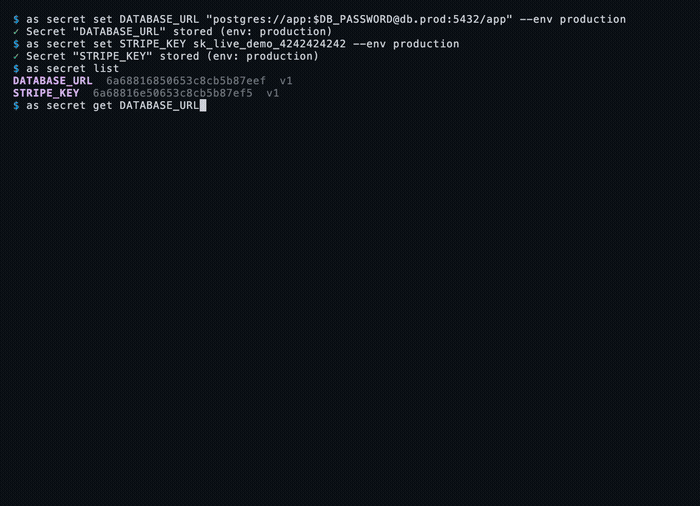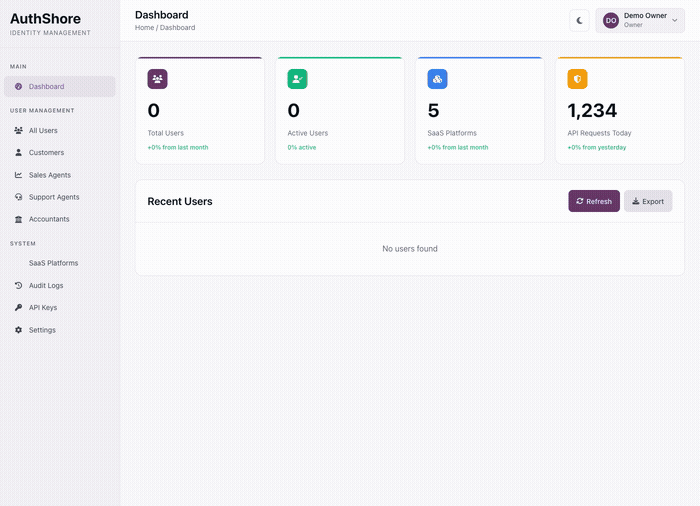](https://prodmedia.tyga.host/public/tyga.cloud/landing/authshore.ai/demo/secrets-demo.mp4) | [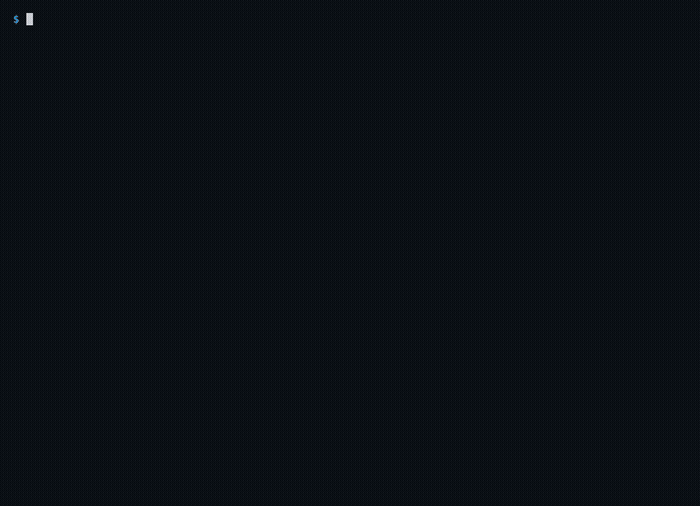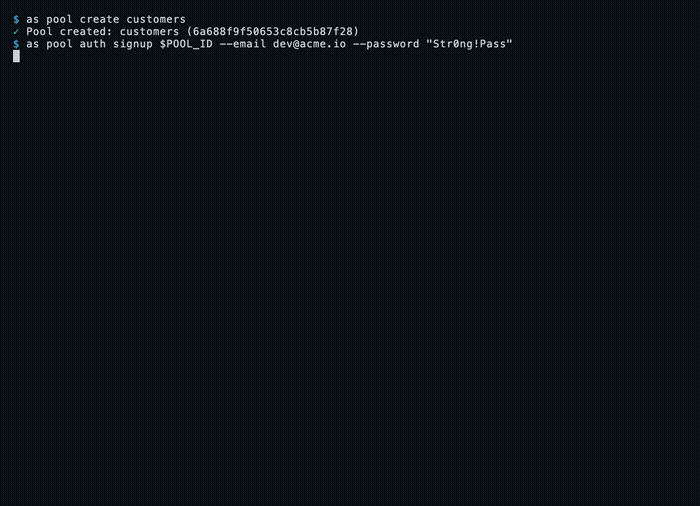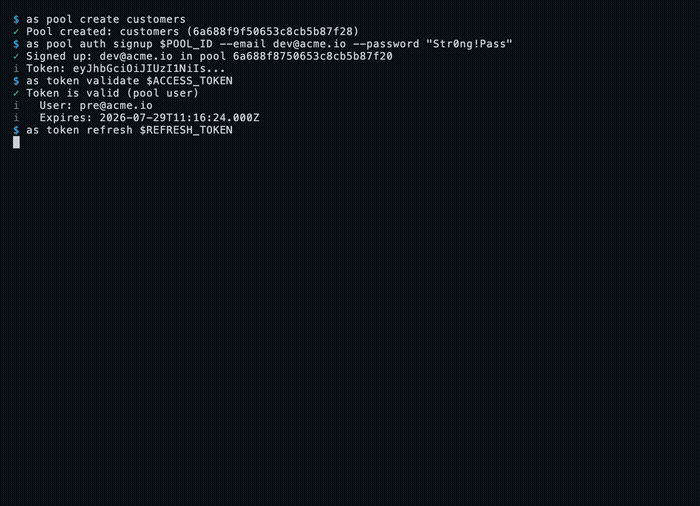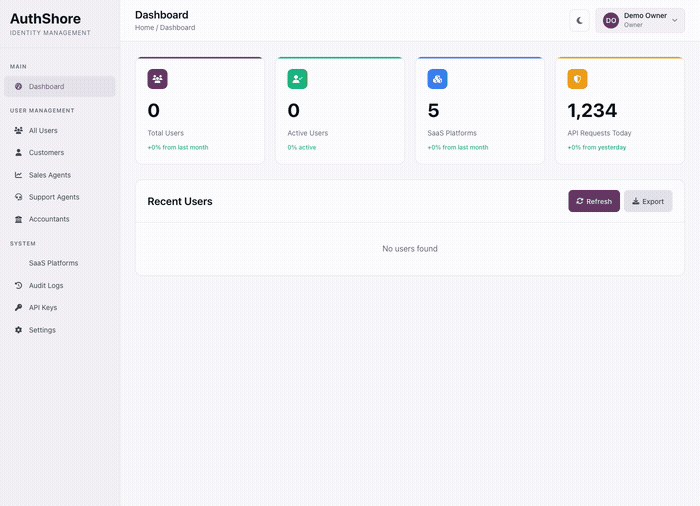](https://prodmedia.tyga.host/public/tyga.cloud/landing/authshore.ai/demo/tokens-demo.mp4) |
More demos: [authshore.ai/#demo](https://authshore.ai/#demo)
## Install
```bash
npm install -g authshore
```
The npm package is `authshore`; the command is `as`.
## Quick Start
```bash
# 1. Create a project — free plan, API key active immediately, no card
as signup my-project --email you@example.com --local
# 2. Create a user pool
as pool create main
# 3. Store a secret (encrypted at rest, versioned)
as secret set DATABASE_URL "postgres://user:pass@host:5432/db"
# 4. Sign up a user in your pool
as pool auth signup main --email user@example.com --password SecurePass123!
# Full reference
as help
```
## User Pools — Cognito without the console
Every project gets isolated user pools your agent manages from the terminal: create pools, add users, run full signup/signin flows that return real JWT pairs.
```bash
as pool create main # create a pool
as pool list # list pools
as pool users <id> # list users in a pool
as pool user add <id> --email E --password P
as pool auth signup <id> --email E --password P # returns access + refresh tokens
as pool auth signin <id> --email E --password P
```
## Secrets Vault — stop pasting keys into .env
Encrypted, versioned key-value storage scoped to your project. Your agent stores third-party keys once and reads them at deploy time — nothing sensitive left sitting in the repo.
```bash
as secret set STRIPE_KEY "sk_..." --env production
as secret get STRIPE_KEY # decrypted read
as secret list
as secret versions STRIPE_KEY # full version history
as secret delete STRIPE_KEY
```
## Tokens — mint, validate, refresh, revoke
The JWT plumbing agents usually hand-roll, done right once.
```bash
as token validate <jwt> # verify signature + expiry, show claims
as token refresh <refresh-token> # rotate the pair
as token revoke <token> # kill a compromised token
```
## MCP Server
Prefer tools over a CLI? `as` ships an MCP server. Point Claude Code (or any MCP client) at it and your agent gets **18 native tools**: pools, users, secrets, tokens, project status.
```bash
claude mcp add authshore --env AUTHSHORE_API_KEY=as_your_key_here -- as mcp-serve
```
For clients that use a JSON config (Cline, Cursor, Windsurf), pass your API key via the `AUTHSHORE_API_KEY` environment variable. The MCP server runs outside your project directory, so it will not pick up `.authshore/config.json`:
```json
{
"mcpServers": {
"authshore": {
"command": "as",
"args": ["mcp-serve"],
"env": { "AUTHSHORE_API_KEY": "as_your_key_here" }
}
}
}
```
No key yet? `as signup my-project --email you@example.com` provisions one in seconds — free plan, no card.
### Remote MCP — zero install
No CLI at all? Claude Web, Claude Desktop, Raycast, or any hosted MCP client can connect straight to our remote server. Same 18 tools, nothing to install:
```
URL: https://mcp.authshore.ai/sse
Auth: Authorization: Bearer YOUR_API_KEY
```
No key? Connect without one: the remote server starts in onboarding mode with an `authshore_signup` tool that provisions your account and unlocks everything in the same session.
## Features
- **User pools** - isolated pools per project, full signup/signin flows, real JWT pairs
- **Secrets vault** - encrypted at rest, versioned, environment-scoped
- **Tokens** - validate, refresh, revoke from the terminal
- **MCP server** - 18 tools, local (`as mcp-serve`) or fully remote (`mcp.authshore.ai`): Claude Code, Claude Web, Cursor, Raycast, any MCP client
- **Agent-first CLI** - `--json` on every command for programmatic parsing
- **Project-local config** - `.authshore/config.json`, auto-loaded, gitignore-friendly
**Pricing:** free plan with an instantly-active API key — no card, no trial clock. Paid plans (Starter $9 / Pro $29 / Scale $99 per month) come with a 7-day free trial via secure Stripe checkout. [Details](https://authshore.ai/#pricing).
## Config
```bash
as login --key YOUR_KEY --local # saves to .authshore/config.json (project-local)
as config # show active config
as me # identity check: which project am I?
```
API key is resolved in this order (highest priority first):
1. `--key` flag
2. `AUTHSHORE_API_KEY` environment variable
3. `./.authshore/config.json` (project-local)
4. `~/.authshore/config.json` (global)
Add `.authshore/` to your `.gitignore`.
## Agent Integration
Add to your CLAUDE.md, .cursorrules, .clinerules, .windsurfrules, or AGENTS.md:
```
## Auth
This project uses AuthShore for auth: user pools, secrets, tokens.
Use the `as` CLI. Config is in .authshore/config.json (auto-loaded).
If not configured: as login --local --key YOUR_KEY
Run `as help` for the full command reference. Run `as me` before any writes.
```
## Why this exists
Every agent-built app hits the same wall: auth. I watched my agents hardcode secrets, reinvent JWT refresh, and stall on Cognito consoles they can't click. So I built the auth layer the agent runs itself. It's early and I'm iterating fast: if something's rough or missing, [open an issue](https://github.com/jyswee/authshore/issues) — I read every one.
## Documentation
- [Quickstart Guides](https://authshore.ai/docs/quickstart.html)
- [Full Reference](https://authshore.ai/llms.txt)
- [Status](https://authshore.ai/health)
## License
Proprietary - Tyga.Cloud Ltd. See [LICENSE](./LICENSE).