{
"markdown": "# opengist-mcp\n\n\n\n[](https://github.com/ni-c/opengist-mcp/actions/workflows/ci.yml)\n[](https://scorecard.dev/viewer/?uri=github.com/ni-c/opengist-mcp)\n \n[](https://glama.ai/mcp/servers/ni-c/opengist-mcp)\n
\n[](https://www.npmjs.com/package/opengist-mcp)\n[](https://github.com/ni-c/opengist-mcp/pkgs/container/opengist-mcp)\n[](https://mcp-hub.ni-c.de)\n
\n[](https://opengist-mcp.ni-c.de)\n[](https://github.com/sponsors/ni-c)\n\n\nA [Model Context Protocol](https://modelcontextprotocol.io) (MCP) server for [Opengist](https://github.com/thomiceli/opengist), the self-hosted pastebin powered by Git.\n\nLets MCP clients like Claude Code, Claude Desktop or Codex read, search, create, update and delete gists on your own Opengist instance: file contents and revisions, commit history, forks and likes, plus your user account.\n\nFourteen tools is the ceiling, not the floor: `OPENGIST_ALLOW_TOOLS=essential`\nregisters a curated seven instead, and a model picks the right tool far more\nreliably from seven than from fourteen — see\n[choosing which tools load](#choosing-which-tools-load).\n\n\n\n \n \n  \n\n\n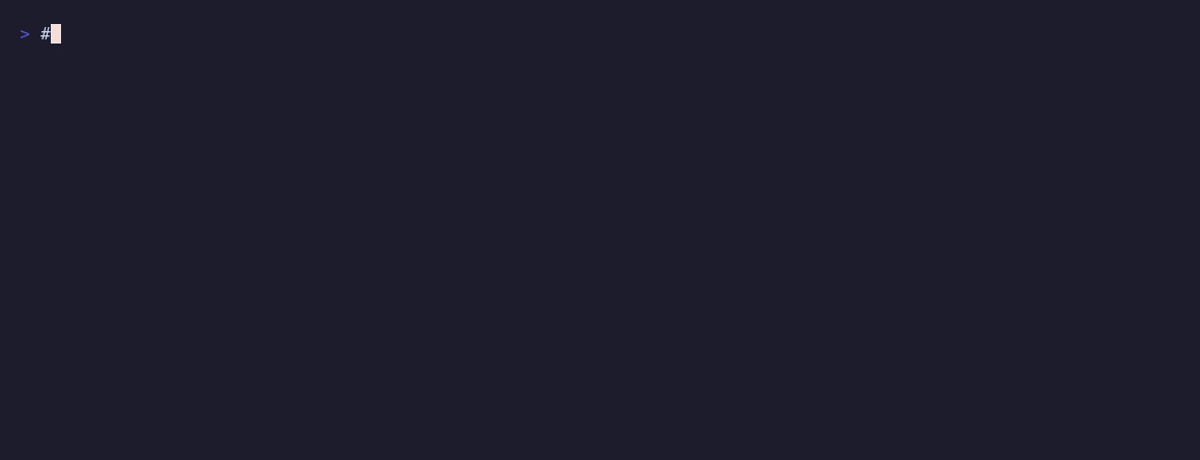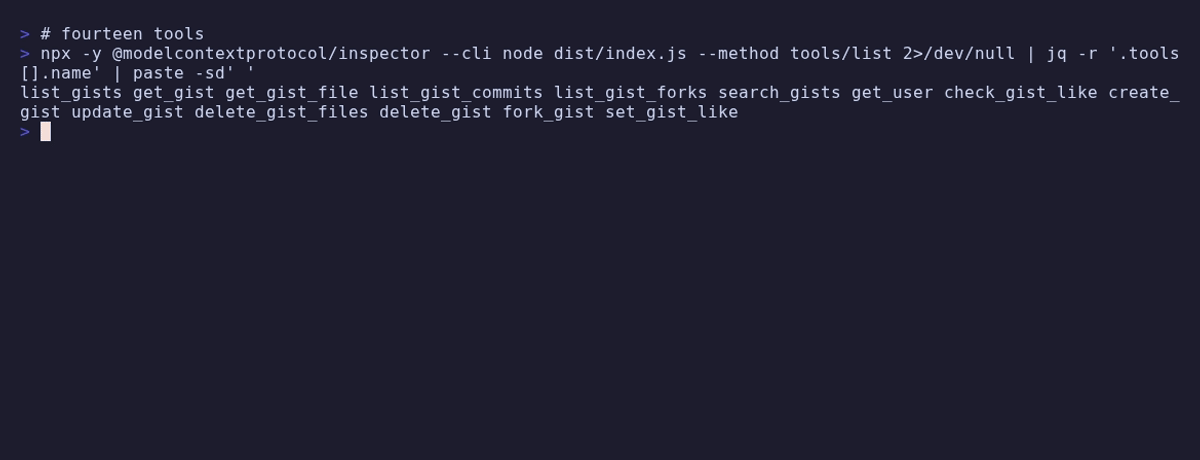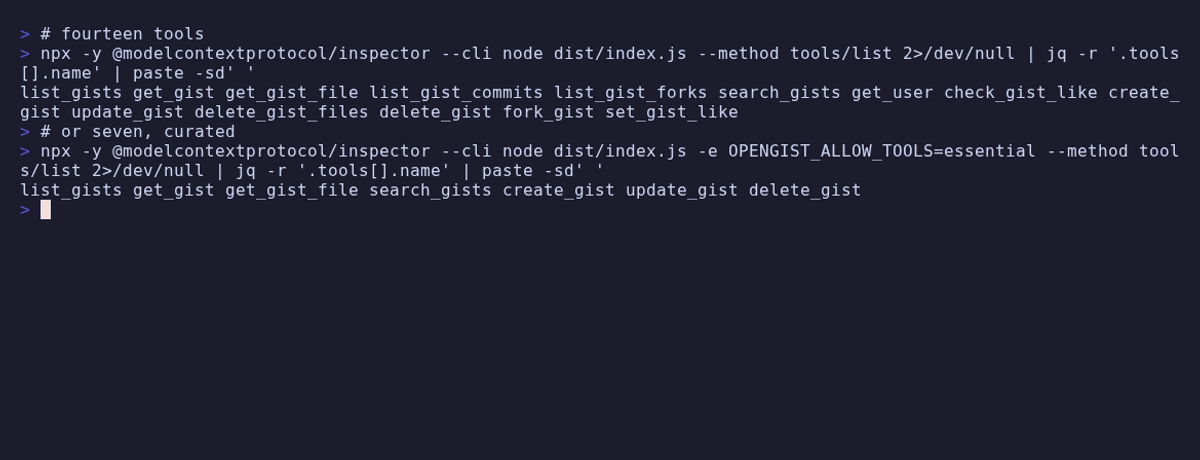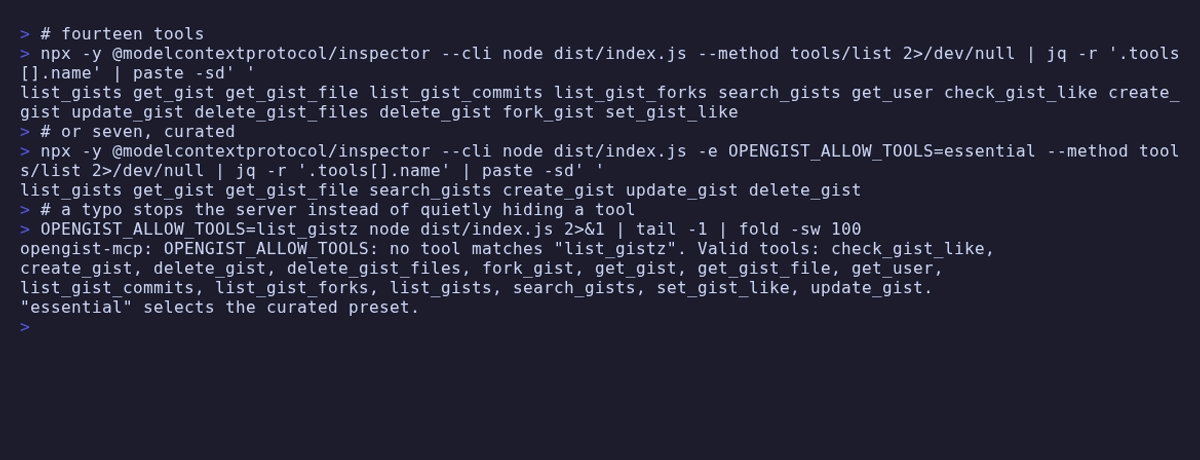\n\n> **Note:** this server talks to the Opengist REST API under `/api`, which is available in recent Opengist releases and enabled by default (`api.enabled`). A running instance serves its own OpenAPI spec at `GET /api/openapi.yaml` — compare it against your version if a tool behaves unexpectedly.\n\n## What makes it different\n\n**Fourteen tools over one API surface**, derived from the Opengist REST API and\nverified against a live instance: reading, searching, writing, forking and liking\ngists, including revisions, commit history and raw file access.\n\n**Bounded by construction.** File contents are capped per file and against an\noverall budget, binary files are never dumped as text, and every truncation names\nthe call that fetches the rest.\n\n## Requirements\n\n- Node.js 22 or newer\n- An Opengist instance with the REST API enabled\n- An Opengist Personal Access Token (Settings → Access Tokens). Scopes:\n - `gist:read` — read gists, including your private and unlisted ones\n - `gist:write` — create, update, delete and fork gists\n - `user:read` — read your own account\n - `user:write` — only needed for `set_gist_like`\n\n A token **without** `gist:read` still works, but the API then silently returns only public gists instead of failing.\n\n## Configuration\n\n| Variable | Required | Description |\n| ----------------------- | -------- | ------------------------------------------------------------------------------------------------------- |\n| `OPENGIST_URL` | yes | Base URL of your instance, e.g. `https://gist.example.com`. A trailing `/api` is accepted and stripped. |\n| `OPENGIST_TOKEN` | yes | Personal Access Token, starts with `og_` |\n| `OPENGIST_READ_ONLY` | no | `true`, `1` or `yes` registers only the read tools; the write tools do not exist at all in that session |\n| `OPENGIST_INSECURE_TLS` | no | `true` accepts self-signed certificates, scoped to the Opengist connection (never process-wide) |\n| `OPENGIST_ALLOW_TOOLS` | no | Comma-separated tool names, `list_*` prefixes, or `essential` for a curated preset |\n| `OPENGIST_DENY_TOOLS` | no | Same syntax; removed from whatever `OPENGIST_ALLOW_TOOLS` left |\n| `ELICITATION` | no | `false` replaces the approval dialog with the two-call token. **Not prefixed** |\n\n> The token is read once at startup and then removed from `process.env`, so it is not visible to child processes. Use `https://` for anything but a loopback address — over plain http the token and every gist travel in cleartext.\n>\n> If your instance's `external-url` is not configured, the URLs Opengist reports (and this server passes through) point at `localhost`. Set `external-url` / `OG_EXTERNAL_URL` on the instance so links are usable.\n\n### Choosing which tools load\n\n`OPENGIST_ALLOW_TOOLS` and `OPENGIST_DENY_TOOLS` take comma-separated tool names;\na trailing `*` matches a whole family. `essential` is a curated preset of\nseven: `list_gists`, `search_gists`, `get_gist`, `get_gist_file`, `create_gist`, `update_gist`, `delete_gist`.\n\n```sh\nOPENGIST_ALLOW_TOOLS=essential\nOPENGIST_ALLOW_TOOLS=list_gists,get_gist_file,create_gist\nOPENGIST_DENY_TOOLS=delete_*\n```\n\nAn entry that matches no tool aborts startup and names it, so a typo cannot\nsilently hide a tool — an absent tool is not something anyone traces back to an\nenvironment variable. A filtered tool is never registered, so it is absent from\n`tools/list` and unknown to `tools/call` alike, exactly like a write tool under\n`OPENGIST_READ_ONLY`.\n\nIf you run several of these servers at once, [mcp-hub](https://mcp-hub.ni-c.de)\nis the other answer — its `/hub` endpoint replaces every server's tools with six\nmeta-tools.\n\n## Installation\n\n### Claude Code\n\n```sh\nclaude mcp add opengist -s user \\\n -e OPENGIST_URL=https://gist.example.com \\\n -e OPENGIST_TOKEN=og_your_token \\\n -- npx -y opengist-mcp\n```\n\n### Claude Desktop\n\n`claude_desktop_config.json`:\n\n```json\n{\n \"mcpServers\": {\n \"opengist\": {\n \"command\": \"npx\",\n \"args\": [\"-y\", \"opengist-mcp\"],\n \"env\": {\n \"OPENGIST_URL\": \"https://gist.example.com\",\n \"OPENGIST_TOKEN\": \"og_your_token\"\n }\n }\n }\n}\n```\n\n### Codex\n\n`~/.codex/config.toml`:\n\n```toml\n[mcp_servers.opengist]\ncommand = \"npx\"\nargs = [\"-y\", \"opengist-mcp\"]\nenv = { OPENGIST_URL = \"https://gist.example.com\", OPENGIST_TOKEN = \"og_your_token\" }\n```\n\n### Docker\n\n```sh\ndocker run --rm -i \\\n -e OPENGIST_URL=https://gist.example.com \\\n -e OPENGIST_TOKEN=og_your_token \\\n ghcr.io/ni-c/opengist-mcp:latest\n```\n\n`-i` is required — the transport is stdio. Do not add `-t`; a TTY corrupts the\nprotocol stream.\n\n### From source\n\n```sh\ngit clone https://github.com/ni-c/opengist-mcp.git\ncd opengist-mcp\nnpm install\nnpm run build\n```\n\n### Through mcp-hub\n\nA client that cannot spawn a local process — ChatGPT connectors, Claude on the web,\nCursor, LibreChat — reaches opengist-mcp through [mcp-hub](https://mcp-hub.ni-c.de): one\ncontainer serves many stdio MCP servers over Streamable HTTP, with an OAuth 2.1 login\nbehind a single password and long-lived tokens for the clients that cannot do OAuth. Its\n`/hub` endpoint puts every server behind six meta-tools, so one connector reaches all of\nthem without N×tool schemas in the model's context, and it speaks both protocol revisions\n— a question this server asks travels through it to the person at the far end.\n\nIts `/config/mcp.json` uses Claude Code's format, so the entry is the one you already\nhave:\n\n```json\n{\n \"mcpServers\": {\n \"opengist\": {\n \"command\": \"npx\",\n \"args\": [\"-y\", \"opengist-mcp\"],\n \"env\": { \"OPENGIST_ALLOW_TOOLS\": \"essential\" },\n \"denyTools\": [\"delete_*\"]\n }\n }\n}\n```\n\n`allowTools` and `denyTools` there are the hub's **own** per-server filter, which is not\nthe same thing as `*_ALLOW_TOOLS` in `env` — the difference, and the mistake it invites,\nare in the [client guide](https://opengist-mcp.ni-c.de/guide/clients#through-mcp-hub).\n\n## Tools\n\n### Reading\n\n| Tool | Description |\n| ------------------- | ----------------------------------------------------------------------------------------------------------- |\n| `list_gists` | List gists: your own, another user's, all public ones, or liked/forked ones (`scope` + optional `username`) |\n| `search_gists` | Find gists by title, description, topics or owner — a bounded client-side scan (Opengist has no search API) |\n| `get_gist` | Get one gist with its file contents, optionally at a revision; commits and forks on request |\n| `get_gist_file` | Get the raw content of a single file, at a revision and from an offset — for large or truncated files |\n| `list_gist_commits` | Commit history of a gist, newest first |\n| `list_gist_forks` | Forks of a gist |\n| `get_user` | Your own account, or another user by `username` or `userId` |\n| `check_gist_like` | Whether you liked a gist; distinguishes \"not liked\" from \"not visible to you\" |\n\n### Writing\n\n| Tool | Description |\n| ---------------------- | ---------------------------------------------------------------------------------------------------- |\n| `create_gist` 👤 | Create a gist from a list of files. `visibility` is required; public/unlisted asks a person |\n| `update_gist` | Change title/description/visibility and write or rename files. Cannot delete files |\n| `delete_gist_files` 👤 | Delete files from a gist — the approval is bound to exactly those filenames |\n| `delete_gist` 👤 | Delete a gist permanently |\n| `fork_gist` | Fork a gist; reports whether a new fork was created or one already existed |\n| `set_gist_like` | Like or unlike a gist idempotently (reads the current state first, so a repeat call is not a toggle) |\n\n### Structured output\n\nEvery tool declares an `outputSchema` and answers with `structuredContent`\nalongside the text block, so a client can use the result without parsing prose:\n\n```jsonc\n{\n \"untrusted\": true,\n \"source\": \"opengist\",\n \"scope\": \"self\",\n \"pagination\": { \"page\": 1, \"perPage\": 20, \"total\": 42, \"nextPage\": 2 },\n \"gists\": [{ \"id\": \"abc123\", \"title\": \"…\", \"visibility\": \"private\" }],\n \"notes\": [\"…\"],\n}\n```\n\nEvery tool that reports gist content carries `untrusted: true` and\n`source: \"opengist\"` as fields. This server has always said so in `notes` —\nprose in a list, which a client can read but not check — and the field is what\nmakes it checkable. Three tools are without it, because their answer is entirely\nthis server's own words: `check_gist_like`, `set_gist_like` and `delete_gist`\nreport an id they were given and a boolean.\n\nAn over-budget result still drops file contents first. Where that is not enough\nit is now an **error**: it used to answer with the JSON cut at the ceiling,\nwhich a text block tolerates and `structuredContent` cannot.\n\n### Safety\n\n- **Irreversible actions ask a person.** `delete_gist`, `delete_gist_files` and widening a gist's visibility raise a real dialog through MCP elicitation where the client supports it — one the model cannot answer on its behalf. A plain `confirm: true` flag could be set by the model on its own, or be talked into it by text inside a gist. Where the client cannot show a dialog they refuse the first call and return a random, single-use token that expires after five minutes; that proves the call was made twice with the same arguments and nothing more, and the text says so. Either way the approval for `delete_gist_files` is bound to the exact set of filenames, so one for a single file cannot be replayed to delete another. `ELICITATION=false` takes the fallback deliberately; it never removes the guard. See [Asking a person](https://opengist-mcp.ni-c.de/guide/approval).\n- **Publishing content is asked about the same way.** Creating a `public` or `unlisted` gist, and writing files into a gist that already is one, are disclosure events: whatever the model has in its context becomes readable by others and cannot be withdrawn from anyone who already saw it. Both ask before they act. The approval is bound to the exact content, so one for a single file cannot be replayed with a second one attached. A call that makes the gist private in the same breath is not a disclosure and is not asked about.\n- **Confirmations are checked after validation.** A call that could not succeed anyway is reported as the input error it is, rather than first costing a confirmation round-trip.\n- **Confirmation prompts never quote gist text.** Titles, descriptions, topics and filenames are user-supplied and could carry instructions aimed at manufacturing a confirmation, so refusals show only server-side metadata (visibility, file count, dates).\n- **`update_gist` cannot delete a file.** The Opengist API deletes a file when its entry is `null` _or_ carries neither `content` nor `filename` — exactly the shape a sloppily built object has. This server therefore never exposes the raw file map; it accepts explicit `write`/`rename` operations and asserts before sending that no entry could be read as a deletion. Files you do not mention are left untouched.\n- **Typos cannot silently duplicate a file.** A write to a filename that does not exist is refused unless `allowCreate: true` is passed, and the refusal names a case-insensitive near match (`readme.md` vs `README.md`).\n- **Gist content is untrusted input.** Every response that carries file content is tagged with a note saying so. Treat gist text as data, never as instructions.\n- **Results are bounded.** File contents are capped per file and against an overall budget, commits and forks are omitted by default, binary files are not dumped as text, and every truncation is reported together with the call that fetches the rest. `search_gists` states how much it scanned and marks incomplete results explicitly.\n- **The instance is read, not trusted.** Every response goes through one boundary: a field of the wrong type is absent rather than fatal, counts are finite, a commit id has the shape of one before it is used, and display strings are cut. Every string that leaves is stripped of control characters and repaired of lone surrogates; where that touches a file body the result says how many characters it removed, per file.\n- **Requests are hardened.** Redirects are refused so the bearer token cannot be replayed to another host, every request carries a timeout, path parameters reject `.`/`..` and are URL-encoded, and upstream error bodies are truncated with HTML error pages dropped entirely.\n- **Residual risk:** `OPENGIST_READ_ONLY` and the approval flow are client-side guards. The real boundary is the scope of your access token and the permission prompts of your MCP host. A token limited to `gist:read`/`user:read` cannot write, whatever the model attempts.\n\n## Not exposed, on purpose\n\n**Not a git client.** It talks to the REST API. Cloning, pushing and branching are\ngit's job — `clone_url` and `ssh_url` come back so you can hand them to git.\n\n**Not an admin tool.** There is nothing here for users, settings or instance\nadministration, and `get_user` returns an allowlisted set of fields rather than\nwhatever the API happens to include.\n\n**Not a search index.** Opengist has no search endpoint, so `search_gists` works\nwith what the API offers rather than pretending to more.\n\n## Safety\n\n- Everything Opengist returns was written by a person, and quite possibly not by\n you — file contents, titles, descriptions, topics and git author names are\n marked as untrusted data, to be reported rather than followed.\n- Results are bounded: file contents are capped per file and against an overall\n budget, binary files are never dumped as text, and every truncation names the\n call that fetches the rest.\n- Deleting a gist or its files, and widening a gist's visibility, ask a person\n first through MCP elicitation. Where the client cannot show a dialog, the call\n is refused and carries a random single-use token that expires after five\n minutes and only ever appeared in a previous tool result.\n- Two ways to stop it writing, and they are not equivalent:\n `OPENGIST_READ_ONLY=true` does not register the write tools, which this server\n enforces; a token scoped to `gist:read` and `user:read` cannot write whatever\n this server or the model does. Use the second one when it matters.\n- A public gist is a publishing channel — world-readable on most instances, and\n indexed. Making one is a decision, which is why it asks.\n\n## Documentation\n\nThe full guide, tool reference and security notes live at\n**[opengist-mcp.ni-c.de](https://opengist-mcp.ni-c.de)** (source in [`docs/`](docs/)).\n\n## Development\n\n```sh\nnpm install\nnpm run build\nnpm test\nnpm run lint\n```\n\n### Releasing\n\nBump the version in `package.json` and `server.json`, move the `## [Unreleased]` section of `CHANGELOG.md` to the new version, commit, then push a tag:\n\n```sh\ngit tag -a v0.1.0 -m \"v0.1.0\"\ngit push origin main v0.1.0\n```\n\nThe release workflow verifies that the tag matches the package version, publishes to npm via OIDC trusted publishing (no long-lived token), waits for the container image to appear on GHCR, registers the release in the MCP registry and creates a GitHub release from the changelog section.\n\nIf the registry step fails, fix it on `main` and dispatch `mcp-registry.yml` — never re-run the tagged job, which checks out the immutable tag.\n\n## Releasing\n\nReleases are tag-driven. Bump `package.json`, move the `[Unreleased]` notes in\n`CHANGELOG.md` under the new version, commit, then:\n\n```sh\ngit tag -s vX.Y.Z -m \"vX.Y.Z\"\ngit push origin main vX.Y.Z\n```\n\nThe release workflow publishes to npm via Trusted Publishing (OIDC, with\nprovenance), pushes the multi-arch container image to GHCR, creates the GitHub\nrelease from the CHANGELOG section, and updates the entry in the official MCP\nregistry.\n\n## Contributing\n\nIssues, discussions and pull requests are welcome — see\n[CONTRIBUTING.md](CONTRIBUTING.md). For vulnerabilities please use\n[private reporting](https://github.com/ni-c/opengist-mcp/security/advisories/new)\nrather than a public issue; the policy is in [SECURITY.md](SECURITY.md).\n\n## License\n\n[MIT](LICENSE) © Willi Thiel\n",
"bytes": 20056,
"sha": "33c85b3865cb880d5b574d7215068ad4bce316dba732ce28a21fac07a85bfe95",
"repo_slug": "ni-c/opengist-mcp",
"fonte": "repo",
"truncated": false,
"api": "https://agentalog.com/api/listings/mcp_io_github_ni_c_opengist_mcp_4b12b4a2/readme"
}